Protect every layer of your mobile application
SecIron secures Android and iOS apps end to end: assess before release, harden the compiled binary with codeless integration, and detect and respond to threats in real time on devices you do not control. Enterprise-grade protection, deployed in days, with no source code changes.
End-to-end mobile app protection, guaranteed.
End-to-end mobile app hardening, without touching your code
SecIron helps enterprises protect mobile applications against reverse engineering, app tampering, runtime attacks, malware and emerging zero-day threats through end-to-end mobile application protection.
Code-free mobile app hardening
Multi-layered encryption, obfuscation, anti-tampering and runtime application self-protection (RASP) applied to the compiled app. No SDK, no source changes, nothing for developers to maintain.
Trusted mobile application security experts
Specialists in mobile application security since 2010, with proven expertise across banking, government, fintech and digital platforms in Asia and beyond.
CI/CD-ready mobile security
Integrate hardening into your existing pipeline without disrupting development. DevSecOps teams automate protection from build to deployment and accelerate secure releases.
Defence against the attacks you don’t know yet
Signature-based detection recognises known attack tooling on sight; behaviour-based detection catches unknown techniques by how they act at runtime. Together they give early warning of zero-day attacks nobody has named yet.
Four solutions. One platform. The whole lifecycle.
Deploy mobile applications faster and secure with a platform built to cover every stage: before release, at build, in the field, and on every device your users hold.
Identify vulnerabilities before release, with remediation guidance to help close security gaps.
Explore IronSCAN
Mobile application security assessment
Thorough inspection of your mobile application. Diagnose and identify vulnerabilities in Android and iOS builds against OWASP, CVE and CWE standards, with remediation guidance for every finding, before release.
Mobile app hardening platform
Defend applications against known and unknown threats. Protect Android and iOS apps against reverse engineering, code tampering, runtime attacks, malware and application cloning with multi-layer, codeless hardening.
Real-time monitoring and response system
Real-time mobile threat monitoring and response. Continuous monitoring with behaviour-based detection, detailed security analytics, attack visibility and automated runtime response across your whole app portfolio.

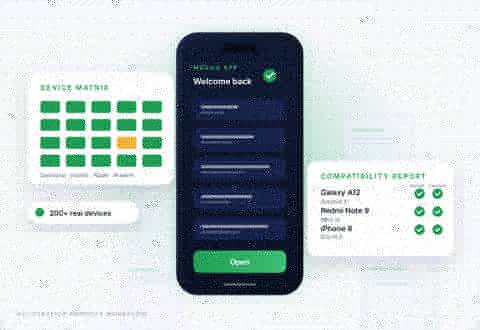
Real-device compatibility testing
Will your app work on every phone your users hold? Install and launch validation across 200+ real physical devices, from older Samsung and Xiaomi models to the latest iPhone, with pass/fail by device within 24 hours and before you go live.
Why your industry needs mobile app hardening
SecIron helps enterprises across banking, financial services, government, e-commerce, healthcare, telecommunications and more secure their mobile applications against reverse engineering, tampering, runtime attacks and emerging threats.
Protect mobile banking, payment and fintech apps against reverse engineering, fraud and runtime attacks, with the audit trail your regulator expects.
Protect citizen-facing applications with app hardening, runtime protection and real-time threat detection.
Secure payment, loyalty and customer applications against tampering, cloning and credential theft.
Stop cheating, memory tampering, modded clients and bot farms from eroding the economy of your game.
Protect the companion apps and control logic that connect devices, sensors and users.
Protect the API keys, session tokens and business logic your mobile client carries to devices you do not own.
Safeguard patient data and healthcare applications with enterprise-grade mobile protection.
Secure connected-car and fleet applications against tampering, spoofing and unauthorised control.
Protect metering, billing and field-service apps that sit on critical infrastructure.
Protect your mobile apps throughout their lifecycle
SecIron applies Adaptive Security Architecture (ASA) principles, combining continuous monitoring, threat intelligence, automation and risk-based decision-making across four continuous phases, with seamless integration into CI/CD pipelines.
Scan the app against OWASP, CVE and CWE standards and fix issues before they ship.
- Harden systems
- Isolate systems
- Prevent attacks
Protect apps from known and unknown attacks, static and dynamic, for continuous security.
- Detect incidents
- Confirm and prioritise risk
- Contain incidents
A real-time security dashboard with the insights needed to guard every app in production.
- Remediate
- Design and model policy change
- Investigate incidents
- Retrospective analysis
Anticipate threats and stop them automatically with minimal disruption to users.
- Anticipate threats and attacks
- Risk-prioritised exposure assessment
- Baseline system and security posture

Ready to strengthen your mobile application security?
Schedule a consultation with our mobile security specialists to discover how SecIron can help protect your applications against today’s most advanced mobile threats.
Mobile app hardening: common questions
What is mobile app hardening?
Mobile app hardening is protection applied to a mobile app after it is built, so it can defend itself on a device you do not control. It combines code protection, anti-tampering, runtime threat detection and response in layers, so an app that gets cloned, repackaged or run on a compromised device detects it and reacts. SecIron applies multi-layer protection without changing your source code.
How is mobile app hardening different from RASP or app shielding?
RASP and app shielding are components of hardening, not alternatives to it. App shielding usually means obfuscation and anti-tampering applied to the package; RASP means runtime self-protection while the app executes. Hardening covers both, plus assessment before release and monitoring after it: one end-to-end process rather than three tools you integrate yourself.
Are developers required to change any code?
No. SecIron is codeless. You submit the built app, protection is applied to the package, and nothing in your repository changes. There is no SDK to integrate, nothing for your team to rewrite, and nothing extra to maintain when you next update the app.
Will mobile app hardening slow our app down?
SecIron is optimised to deliver multi-layer mobile application protection with minimal performance overhead. We measure the impact on your own app during the proof of concept and state it on the record, so you secure your app without compromising speed or usability.
What if an attacker strips the protection out of the app?
The app alerts, or exits. Anti-SDK-removal enforcement is the mechanism most solutions do not have: if the protection layer is removed from the package, the app refuses to run normally rather than running unprotected. It is the difference between protection you have and protection you can prove.
How does mobile app hardening help with BNM RMiT, MAS TRM or FSC requirements?
It gives you both the controls and the evidence. Device binding, anti-screen-capture, malware and rooted-device detection map to the mobile channel considerations referenced in BNM RMiT, MAS TRM, OJK, BSP, Taiwan FSC and HKMA CFI guidance, and IronSKY’s incident log is the audit trail your examiner asks for.
What should I look for in a mobile app hardening solution?
Look for comprehensive app hardening, runtime protection, threat detection, support for Android and iOS, seamless CI/CD integration and expert technical support. Choosing the right platform helps ensure long-term protection against evolving mobile threats.
Mobile app security insights
Guides, articles and case studies from the SecIron team.

Mobile app hardening vs RASP vs app shielding: where does it stop?
RASP, app shielding and mobile app hardening protect different parts of the same attack. Here is where each one stops.

What is mobile app hardening? A complete guide for security teams
Mobile app hardening protects an app on devices you do not control. What it covers, the layers, and how it is applied.

Detecting mobile app security gaps through vulnerability diagnosis
How a mobile network provider found and closed security gaps in its app through vulnerability diagnosis.
Browse all blog posts, success stories and whitepapers and guides.
Mobile app security insights, in your inbox
Threat research, regulatory updates and practical guidance on protecting mobile applications, written for security, engineering and compliance teams. One email a month, no sales pitch.
End-to-end mobile application security. Assess, harden and monitor Android and iOS apps with codeless integration.